A Security Program Maturity System Built for Real Incidents
This is not awareness training, tool instruction, or compliance education. This is an annual security maturity enforcement program built on the Security Program Governance Standard™ (SPGS), designed to produce measurable program change by forcing organizations to verify — not assume — that foundational controls are strong enough to keep routine security events from escalating. It focuses on eliminating common failure modes before incidents become business-impacting events.
What This Program Delivers
Organizations that adopt this program are not buying content. They are adopting a structured governance system that gives security teams, leadership, and risk owners a common operating standard for proving that foundational controls are working.
The program delivers:
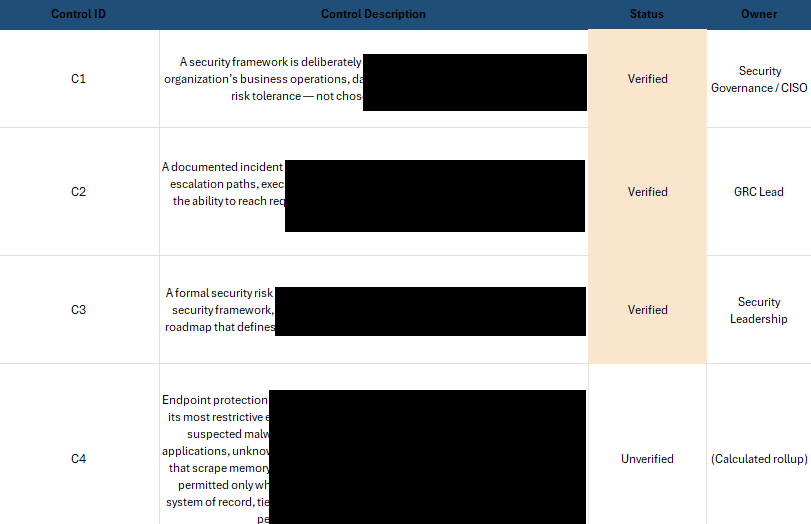
A Program Maturity Tool that evaluates foundational controls, decision authority, and escalation discipline
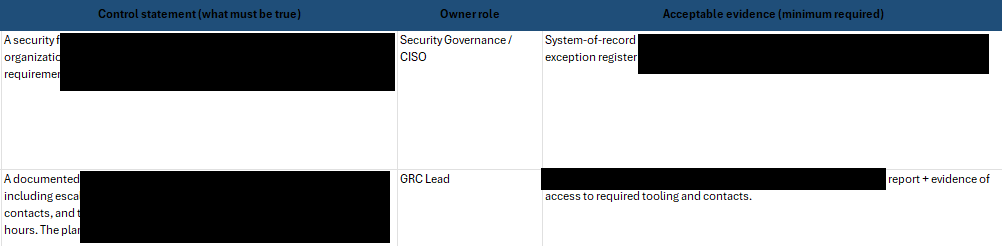
Evidence Requirements & Verification Standards that define what must be proven for a control to be treated as real
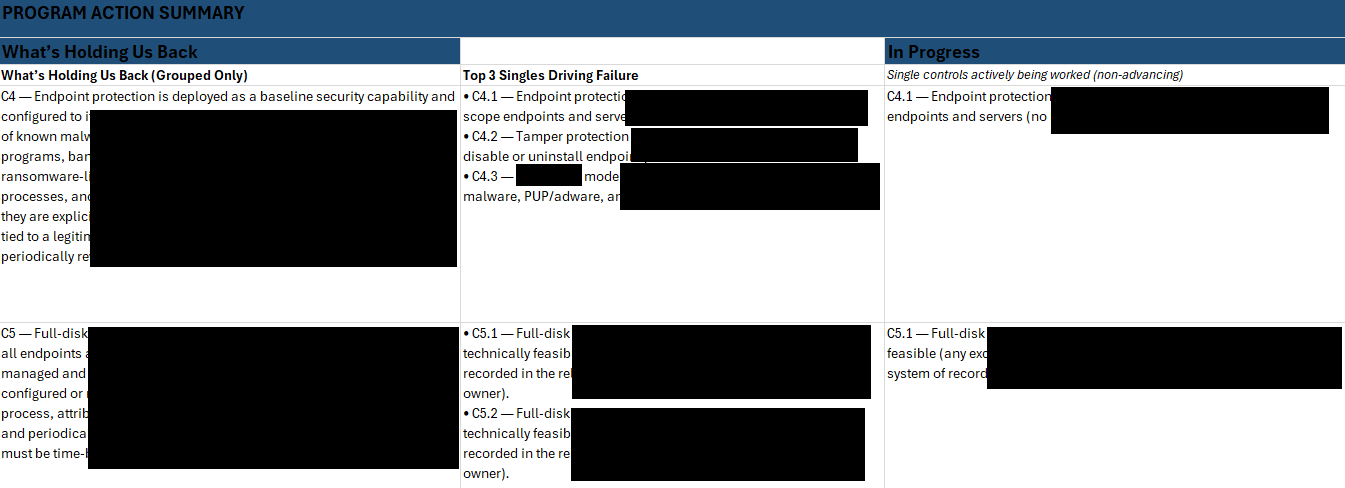
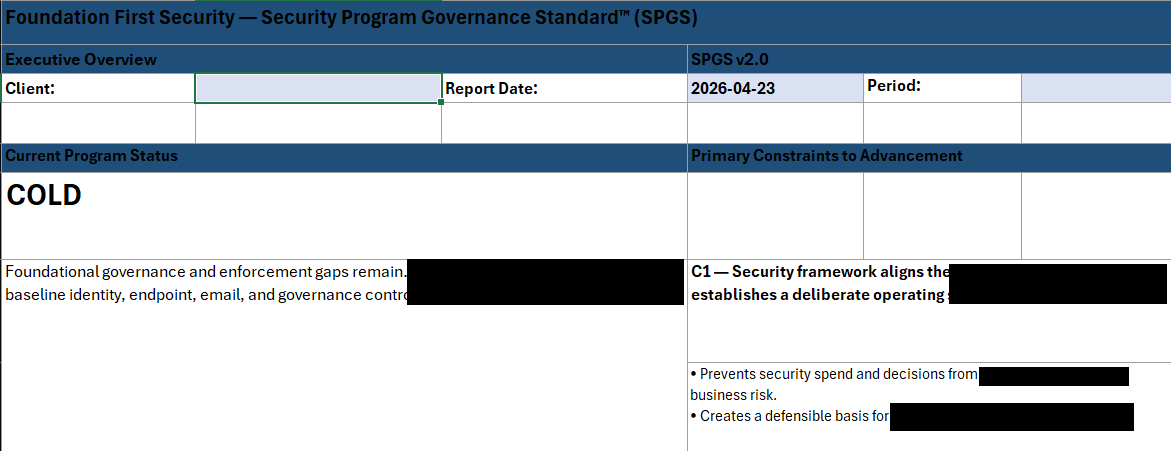
Executive and action outputs that translate technical reality into business accountability
An evidence-based maturity score and executive-ready findings that translate technical reality into business accountability
Explicit decision frameworks that remove ambiguity during containment and response
A repeatable annual verification cycle that reinforces maturity as systems, threats, and leadership change
This program forces clarity where most organizations rely on assumptions.
The Program Maturity Tool
At the center of the program is a security program maturity tool designed to expose gaps that traditional assessments miss. It is delivered in Excel on purpose. Not because it is simple. Because it is usable. Every organization can adopt it immediately. No platform dependency. No tooling rollout. No integration theater. A format both basic and advanced programs can operationalize without delay.
The tool evaluates:
Foundational control effectiveness, not just control presence
Decision-making thresholds under pressure
Authority and escalation clarity
Blast radius by design, not hope
Alignment between security, leadership, and risk owners
Controls are verified, not assumed. Decisions are made explicit, not implied. The output is a clear, defensible view of where the program stands and what actually reduces risk next.
The Program Structure
The program is built from a small number of integrated components that work together to strengthen foundations, improve accountability, and reduce preventable escalation. Together, these components translate security maturity from theory into enforced operational discipline.
Program Maturity Tool
Defines what must be true, exposes what is not, and creates a defensible baseline for maturity and next actions.
Evidence Requirements & Verification Standards
Defines what must be proven before a control can be treated as enforced, keeping maturity tied to evidence instead of self-attestation.
How This Program Prevents Incidents
This program prevents incidents by forcing organizations to design systems that survive failure. It assumes identity will be abused, endpoints will be compromised, users will make mistakes, and controls will degrade over time. By addressing the same failure modes that appear repeatedly in post-incident forensics, By addressing the same foundational failure modes that repeatedly appear in post-incident analysis, the program helps reduce the conditions that allow routine events to become business-impacting incidents before detection and response are required to carry the full burden.
Detection explains failure. Foundational maturity prevents it from cascading.
The Standard Behind the Program
The Security Program Governance Standard™ (SPGS) is the governance standard behind this program. Foundation First Security is the steward, licensing authority, and verification body. That means organizations are not simply buying a model. They are adopting a standard that can be used to operate under a defined governance discipline, verify maturity against explicit evidence requirements, create a repeatable language for leadership, security, and risk owners, and support annual validation and, where applicable, formal verification designations.
SPGS is the governing standard. Foundation First Security distributes the program and performs its evidence-based verification.
An Annual Security Maturity Cycle
Security maturity is not static. The Program Maturity Tool is delivered in a format organizations can use continuously, so maturity can be tracked, updated, and reinforced over time rather than treated as a one-time assessment. Organizations re-engage annually to retest assumptions after organizational or architectural change, validate that foundational controls remain effective, refresh role-based training so leadership, security, and risk owners stay aligned under pressure, and understand how emerging attack patterns interact with the foundations they believe are already in place.
SPGS is reviewed annually and released as a defined version. New versions are issued when substantive changes are warranted. Organizations operate under a defined version for the annual cycle they adopt, making maturity claims and verification designations version-specific and durable.Emerging threat modules are not trend briefings. They are maturity reviews that help organizations understand whether new attack patterns expose weakness in the controls they believe are already strong.
Threats evolve. Failure modes repeat. This cycle is how maturity compounds instead of decaying.
How Teams Use the Program
Security Teams
Verify that foundational controls actually limit blast radius
Develop judgment for containment and escalation
Move from reactive firefighting to deliberate program design
Leadership & Executives
Gain visibility into security maturity without technical noise
Understand tradeoffs before incidents force decisions
Participate in aligned, defensible risk discussions
Legal & Risk Functions
Benefit from explicit escalation paths
Understand how decisions affect exposure and reporting
Align expectations before high-pressure events occur
What This Program Is — and Isn’t
This Program Is:
A security program maturity system
A governance enforcement model
An evidence-based maturity scoring model
A framework for eliminating common failure modes
A bridge between security, leadership, and risk
This Program Is Not:
Awareness training
Phishing simulations
Tool certification
Compliance theater
A SIEM replacement or alerting platform
Deployment Model
The program is designed to integrate into existing operations:
Purchased as an annual engagement
Deployed as an operating model, not a one-time event
Centered on the Program Maturity Tool and Evidence Requirements
Defined evidence review and verification standards
Executive-ready maturity findings and priority actions
Minimal administrative overhead
Organizations typically adopt the program as an annual operating discipline and revisit it after major security, leadership, or architectural change.
Program Snapshots
The program is delivered in Excel on purpose. Not because it is simple. Because it is usable. We’ve included a selection of snapshots from the program to show how it operates in practice: a clear view into how engagement unfolds without requiring translation or interpretation.